Blog
From chaos to control: SailPoint brings autonomous identity security to every human, non-human, and AI agent identity
An AI agent making 10,000 tool calls a second will never wait for an access review. Neither will the attacker who finds the credential it left behind.
That is the gap most identity programs are trying to close right now. According to the latest SailPoint Horizons of Identity Security report, released today, 79% of enterprises already run AI agents in production, yet only 2% have deployed identity security tools built specifically to govern and secure them. And the tools most teams rely on force a bad choice: access reviews that are outdated the moment they finish, or posture dashboards that flag risk but can’t fix it. Seeing a risk and resolving it are two different things. At machine speed, the distance between them is where breaches happen.
Today at Navigate 2026, we’re announcing a major expansion of SailPoint Identity Security that turns identity from a static compliance check into real-time, automated defense, as detailed in our announcement press release.
The announcements span both products in the SailPoint Identity Security solution: SailPoint Agentic Fabric for non-human and agent identities, and SailPoint Human Fabric for your workforce, both running on SailPoint Atlas. The announcement also includes SailPoint IdentityIQ 9.0, a major release for organizations that run identity security on premises or in hybrid environments. The mandate behind all of it is simple. Move from chaos to control and own every identity in your enterprise.
SailPoint Autonomous Agents: Defense that moves at machine speed
When agents invoke MCP tool calls at machine speed, human review of every action is impossible. The common workaround, shutting an agent down the moment something looks unusual, trades one problem for another. It stops the threat, and it stops the business along with it.
SailPoint Autonomous Agents take a different approach. This fleet of specialized AI agents, delivered in three classes, enforces policy, right-sizes privileges, and protects systems across the agentic ecosystem. Because they act on identity context, they can tell legitimate intent from malicious activity. They stop the threat and keep the productive agent running.
A-ISPM: Posture management that fixes what it finds
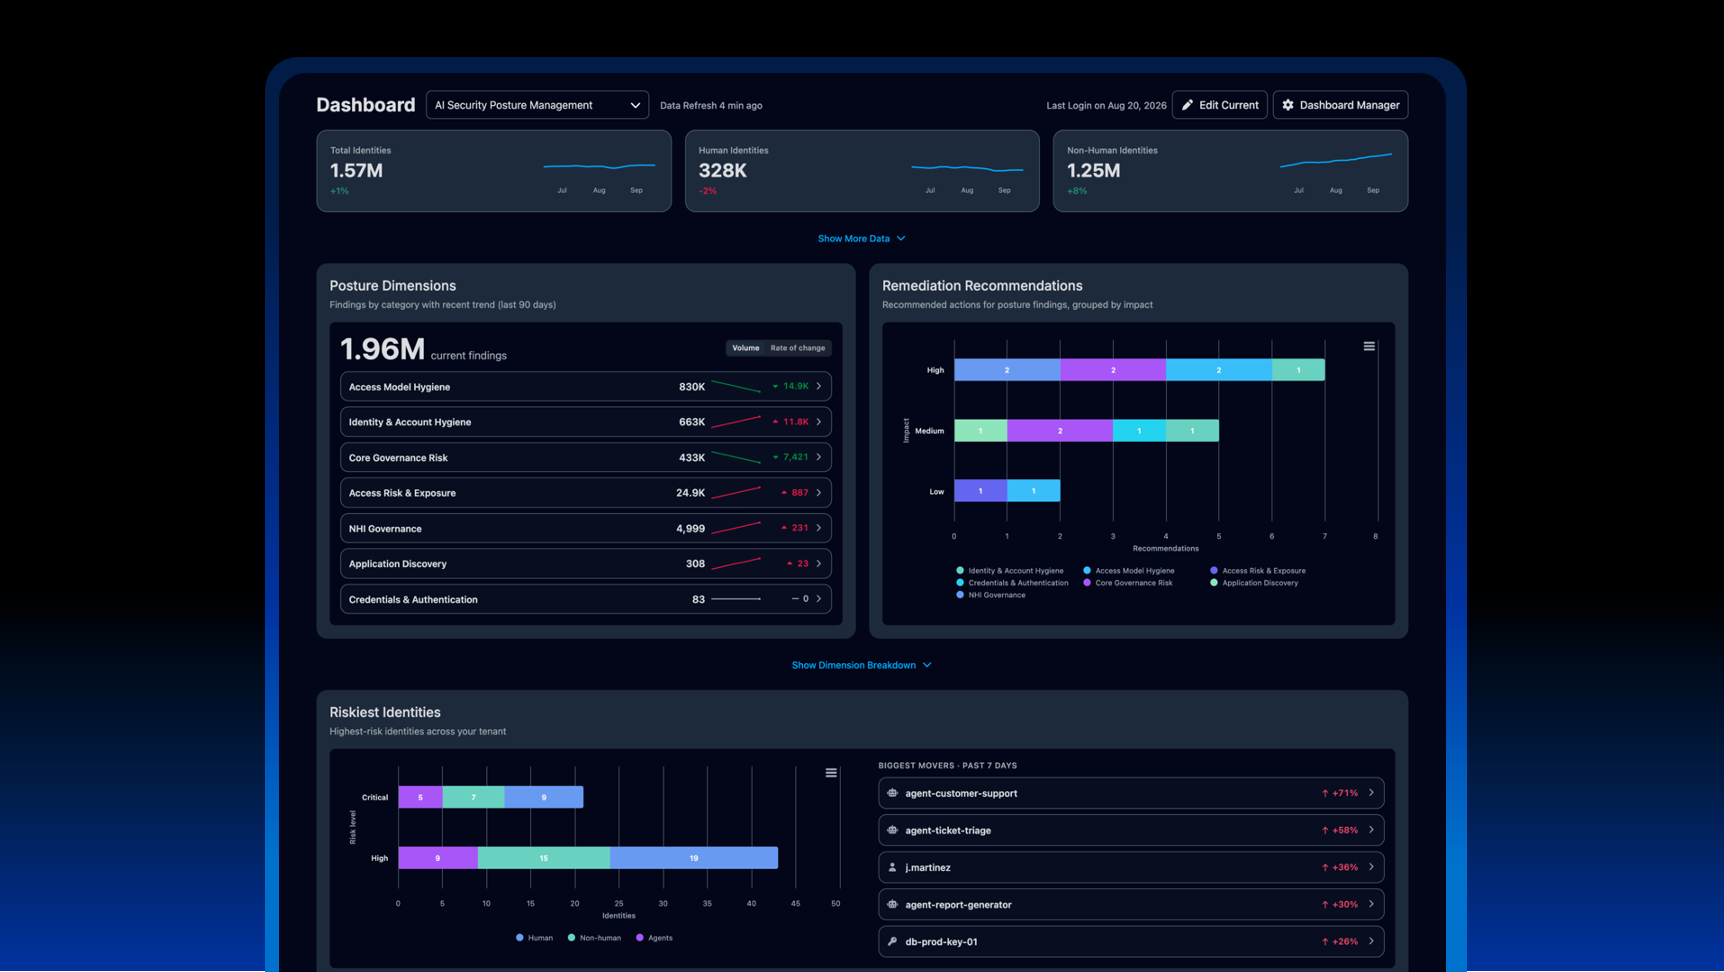
Finding a risk is only half the job. Autonomous Identity Security Posture Management (A-ISPM) is built to finish it. Using the live identity context in SailPoint Atlas, it continuously detects dormant accounts, partially offboarded identities, orphaned access, shadow admins, and privileged outliers hidden deep in access paths. Then it closes the loop on your terms, from one-click fixes such as revoking access, disabling an identity or AI agent, or assigning an owner, all the way to fully automated policy enforcement. A-ISPM is expected in Q4.
More highlights from Navigate 2026
Autonomous Agents and A-ISPM lead the announcement, but they’re only part of the story. Today’s press release covers the full scope of what’s new. Here’s a closer look at the other highlights, and where to go for more detail on each.
Expanded SailPoint Agentic Fabric
Every agent, credential, and data store that never reaches your identity program becomes access no one owns. Expanded SailPoint Agentic Fabric maps the full agentic surface area, including the secrets and credentials agents depend on to run, and uses new endpoint and browser discovery to surface the shadow AI that never went through a security review. We also expect to complete the SailPoint Agentic Fabric and Entro Security integration, one of the fastest in enterprise software history. Entro-powered credential lineage, exposed secret discovery, and prompt intent monitoring will be fully integrated into Agentic Fabric, reaching global general availability in early Q4.
Visibility is only the start. Inline runtime authorization evaluates what an agent is trying to do at the moment it acts, and an agent kill switch stops it the instant it crosses the line. And when auditors ask which agents exist, who owns them, and what they can reach, Agent Audit turns the inventory and governance activity already in Agentic Fabric into framework-aligned evidence you can export on demand or on a schedule. Agentic Fabric runs on the same SailPoint Atlas foundation as your human identity program, so agents and the people behind them are secured together.
Expanded SailPoint Human Fabric
Every new identity adds to the scope of every access review, every policy, and every audit. Expanded SailPoint Human Fabric streamlines that work while giving you finer-grained control over human access. Next-generation access certifications run on a re-platformed engine designed for enterprise-scale access reviews, with no record limits and no need to split large campaigns manually. Next-generation access requests embed SailPoint Harbor Pilot Access Request Agent, so employees ask for what they need in natural language, right from their chat tools.
Advanced separation of duties (SoD) evaluates toxic combinations at the moment of request, including conflicts created by other requests still in flight, and blocks violations before they occur.
Zero Standing Privilege for human and non-human identities
Standing privilege is invisible risk. Every always-on permission, whether it belongs to a person, a service account, or an AI agent, is access an attacker can use without ever breaking in.
New Just-in-Time (JIT) provisioning with conditions, such as business justification or reauthentication, grants privileged access only when it’s needed, with activation through Slack or ServiceNow. Effective privilege visibility calculates the access each identity inherits across nested groups, so you can find where standing privilege hides before you remove it. Together, they replace always-on access for people, service accounts, and AI agents alike.
Enhanced SailPoint Atlas: One foundation for every identity
Autonomous Agents and A-ISPM are only as good as the identity context beneath them. Enhancements to SailPoint Atlas strengthen that foundation and make it easier to build on. New common services give every product on the platform the same shared foundation, and the new Atlas Extensibility framework adds SaaS plug-ins so you can extend SailPoint to fit the way your business runs. Workflow enhancements add versioning, execution history, and serial loops of up to 1,000 iterations, so the automations your team builds are easier to manage, troubleshoot, and scale. The result is a more unified, extensible foundation for scaling identity security.
Atlas also extends your reach to every application, including the ones that have always been hardest to bring into your program. Our new unified connectivity capabilities and video capture for disconnected applications are built for exactly that. Get the details in our unified connectivity blog, with more on governance for disconnected applications to come.
SailPoint IdentityIQ 9.0
Most identity governance infrastructures can’t keep pace with how enterprises operate today, where non-human and AI agent identities work alongside people and bring a new layer of complexity with them. The Human Fabric updates above meet that shift in the cloud. For organizations whose data residency requirements, regulatory constraints, or deeply customized programs make on-premises or hybrid the right fit, IdentityIQ 9.0 delivers the same commitment.
The release reduces risk with time-based access for roles and entitlements, metadata-driven certification campaigns, and Twilio Verify API support for stronger identity verification. UI and UX enhancements make governance easier for business users, and a modernized Jakarta EE foundation keeps IdentityIQ aligned with current enterprise Java standards. A new automated upgrade tool scans your environment and automates much of the manual work, so you can move to the new release with confidence.
Operations innovations for regulated industries and regions
For many organizations, the question isn’t whether identity security belongs in the cloud. It’s whether the cloud can meet the requirements they answer to. Where identity data lives, and which frameworks the service is certified against, can decide whether a program moves forward at all.
We’re expanding where and how SailPoint can serve those organizations. A new South Korea data center region brings local data residency to customers there. Upcoming programs for FedRAMP High and PCI DSS 4.0 extend SailPoint to U.S. federal agencies and contractors with highly sensitive workloads, and to organizations that handle payment card data. An upcoming EU Sovereign Cloud addresses European data sovereignty requirements, and dedicated life sciences programs aligned to GxP and ISO 9001 support the validation and quality standards pharmaceutical and medical device companies work under. For security leaders in highly regulated industries and geographies, that means bringing identity security to the cloud on terms their auditors and regulators recognize.
New Success Acceleration Service Packages
Technology alone doesn’t make an identity program mature. New tiered Success Acceleration Service Packages let you choose the level of support that fits where your program is today. They combine expert-led roadmaps, vertical-specific deployment accelerators, AI-driven risk reduction, and continuous compliance support, so you can reach zero standing privilege and realize value faster.
See it for yourself
Watch the Navigate 2026 keynotes and product demos live or on demand at www.sailpoint.com/navigate, and read the full announcement in today’s press release. To see where your program stands today, take the SailPoint identity security maturity assessment, or connect with a SailPoint identity expert to map your own path from chaos to control.
