Blog
Put your existing data classification to work: How SailPoint and BigID keep sensitive data safe
Modern security leaders understand that identity is the true enterprise security perimeter. Yet, as structured and unstructured data explodes across cloud storage, file shares, and collaboration suites, a lingering visibility gap persists: high-risk data access.
This challenge is intensifying as AI agents, machine accounts, and third-party integrations are querying corporate data repositories at machine speed—often without direct human oversight. When over-privileged identities cross paths with ungoverned, sensitive data, the blast radius of a potential breach multiplies exponentially.
More ways to keep your sensitive data safe
SailPoint Data Access Security already delivers native data discovery and classification across structured and unstructured data estates—utilizing advanced content analysis, customizable pattern logic, dictionaries, and out-of-the-box policies to flag PII, financial records, and proprietary intellectual property.
Now, we're giving organizations even greater flexibility and governance controls to strengthen their existing data security efforts. Today, we're excited to announce that SailPoint customers can now leverage our expanded data classification import capabilities to ingest BigID classifiers directly into SailPoint Data Access Security for enhanced data security.
How it works
For enterprises running BigID to catalog complex data environments, this new integration enables you to ingest your existing BigID classifiers directly into SailPoint Data Access Security. Instead of scanning the same file repositories twice, you can map BigID classifiers to SailPoint data categories to drive identity-centric governance at scale.
- Guided classification import wizard: A streamlined setup wizard connects BigID to SailPoint Data Access Security in minutes, automatically mapping third-party classification labels to corresponding target applications.
- Automated, scheduled ingestion: Recurring, scheduled syncs ensure that classification results remain up-to-date as files, tables, and classification labels evolve.
- Granular, per-application controls: Maintain total control. You can configure each application to run SailPoint’s native classification engine or import classification results from BigID.
- Fast time to value: Access governance starts when classifiers are imported into the SailPoint platform—eliminating the waiting time and infrastructure strain of running full discovery scans from scratch.
Unlock the full power of SailPoint Identity Security
Importing BigID data classification is just the starting point. Once this information is ingested into Data Access Security, it enriches SailPoint’s full suite of identity governance controls, transforming raw metadata into actionable data governance.
Smarter certifications & dynamic access reviews
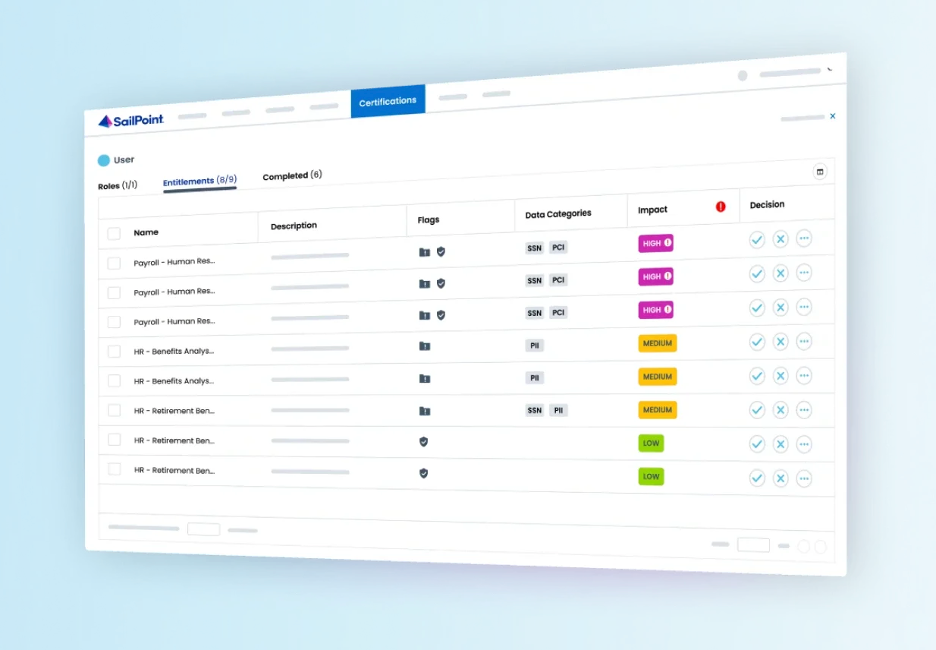
Integrating BigID data classification enriches access reviews with real-time sensitivity context.
- Context-driven decisions: Reviewers see exactly what kind of data an entitlement exposes—such as customer PII, trade secrets, or PCI data—alongside risk scores.
- Dynamic, multi-level approvals: Automatically trigger escalated, multi-level review workflows or require approval when users request access to highly sensitive assets.
- Automated policy denials: Block high-risk access requests outright (e.g., non-employee identities requesting internal-only intellectual property), cutting down on governance fatigue.
Secure the agentic enterprise
You don't need to reinvent your data classification program to achieve enterprise-grade identity security in the AI era. Maximize your existing investments and safeguard your critical data assets from a unified control plane across human, machine, and agent identities.
- See the integration in action: Reach out to your SailPoint account representative or book a demo to explore the full set of capabilities.
- Download the data sheet: BigID data classification import for Data Access Security.
