Deep governance
Enforce precise control over critical assets
Secure critical systems. SailPoint connects directly with your vital enterprise apps to model granular entitlements, enforce SoD, and prevent costly risk.
Beyond basic access
Basic access isn't enough for critical systems
Standard Single Sign-On (SSO) and basic provisioning tell you who can log into an application, but they don't control what users can actually do once inside. Without visibility into fine-grained permissions within complex systems, you expose the business to toxic access combinations, fraud, and compliance failures.
Before SailPoint:
- Blind spots regarding what users can actually do inside complex applications.
- High risk of fraud due to undetected, toxic access combinations (SoD violations).
- Reliance on manual, error-prone IT tickets for complex provisioning tasks.
After SailPoint:
- Complete visibility into deep, transaction-level access and permissions.
- Real-time Separation-of-Duties (SoD) enforcement to proactively block risks.
- Automated, precise provisioning based on strict least-privilege entitlement models.
Granular access control
Secure your critical applications
Advanced governance for your vital enterprise apps
Deploy out-of-the-box connectors designed specifically for complex enterprise applications to expose and control fine-grained permissions.
- Secure critical systems.
- Govern view, edit, and execute permissions beyond login.
- Use pre-built connectors for ERP, CRM, and healthcare applications.
Bring legacy and siloed systems under automated control
Bring applications that lack a modern API under governance.
- Crowdsource onboarding by recording the administrator workflow.
- Automate provisioning.
- Close blind spots on legacy and siloed applications.
get started
See SailPoint in action
Discover how SailPoint Identity Security delivers continuous, intelligent protection for every identity across your enterprise. From real-time governance and automated lifecycle management to Zero Standing Privilege enforcement, see firsthand how leading organizations reduce risk, accelerate compliance, and empower secure innovation.
Success stories
Trusted by leading enterprises
With real results and powerful success stories, we’re redefining what’s possible. From measurable outcomes to game changing impacts, our customers' achievements speak louder than words. See how we’ve helped businesses like yours overcome challenges and unlock their true potential.
Do more with fewer resources
Cut costs while achieving more, see how we make it possible.
Fast, seamless integration
Think it's complex? We simplify it, proven in just weeks.
Reduce the attack surface
Eliminate inactive or orphan accounts vulnerable to attacks.
Related resources
Explore SailPoint connectivity resources

Solution Brief
SailPoint Accelerated Application Management
Learn more about how SailPoint's Accelerated Application Management solution can help your organization get immediate visibility into enterprise application environments, understand deeper application usage insights, and help achieve faster time to value.
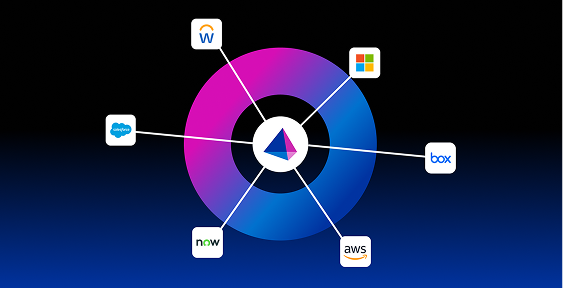
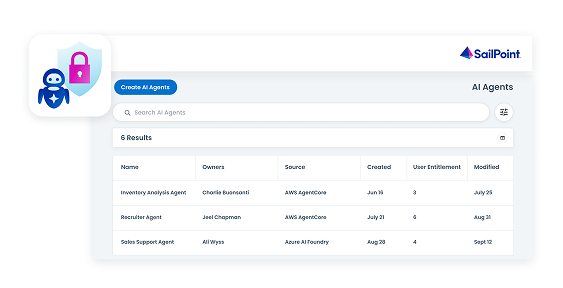
SailPoint connectivity
See what else you can achieve
Deep governance is one part of the model. Discover how to gain total application visibility to eliminate shadow IT, or scale compliance across the applications your business adopts.
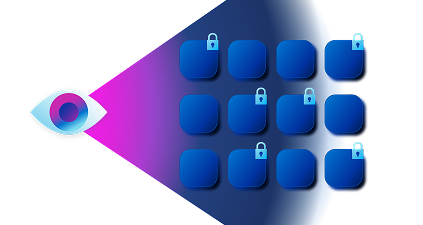
Visibility
Discover unmanaged shadow IT. SailPoint uses lightweight browser extensions and discovery connectors to continuously map your entire application landscape.
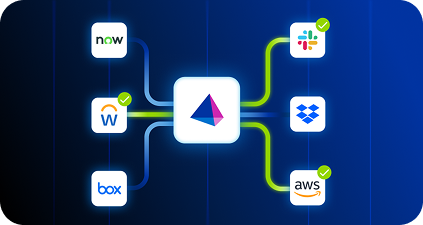
Compliance
Bring applications under governance quickly. SailPoint simplifies connectivity so you can quickly onboard target systems and rapidly scale security controls across your digital workspace.
Frequently asked questions
Common questions about Identity Security Fabric
What is the difference between basic access and "deep governance"?
Basic access, often managed by Single Sign-On (SSO), confirms who can log into an application. Deep governance goes further to control what users can do inside the application. SailPoint's deep governance connectors analyze and manage fine-grained permissions and entitlements, which is essential for securing complex, critical systems.
How does SailPoint handle "disconnected" applications?
For applications that lack modern APIs, SailPoint uses a combination of screen-capture and Robotic Process Automation (RPA). This technology allows you to record the manual steps an administrator would take to manage access and then automates that workflow. This brings even your most difficult-to-integrate legacy and siloed systems under a modern, automated governance model.
Strengthen your defenses with adaptive identity
Detect risk in real time. Continuously monitor identity behavior and surface threats the moment they appear.
Adjust access dynamically. Automatically tighten or grant permissions based on risk, context, and user behavior.
Protect every identity. Secure human, machine, and third-party access across your entire environment.