Navigate 2026 product announcements
The unified identity security fabric
Real-time governance across human and agentic identities to secure the modern enterprise.
Posture Management
Autonomous Identity Security Posture Management (A-ISPM)
Continuously analyze, prioritize, and remediate high-risk identity exposures autonomously.
- Unify posture visibility across human, machine, and AI agent identities.
- Uncover hidden effective privilege, toxic combinations, and hygiene gaps.
- Safely remediate risks with guided 1-click fixes and closed-loop automation.
Non-Human Governance
SailPoint Agentic Fabric
Extend deep identity governance to autonomous AI agents and NHIs. Inspect GenAI prompts, monitor live actions, and safeguard access to underlying critical enterprise data.
- Map full lineage across owners, tokens, credentials, and connected services.
- Detect agent behavioral anomalies and kill active threats at the source (NHIDR).
- Protect GenAI prompts and responses with monitor, redact, and block policies.


Human Governance
SailPoint Human Fabric
SailPoint Human Fabric advances human governance toward real time. This release extends access certifications scale, adds proactive Separation-of-Duties, and enriches access requests.
- Scope campaigns with rich access model metadata and flexible AND/OR logic.
- Separation-of-Duties now prevent conflicts at request, with role-based policies.
- Conversational access requests, now with custom forms in the same flow.
Deep integration
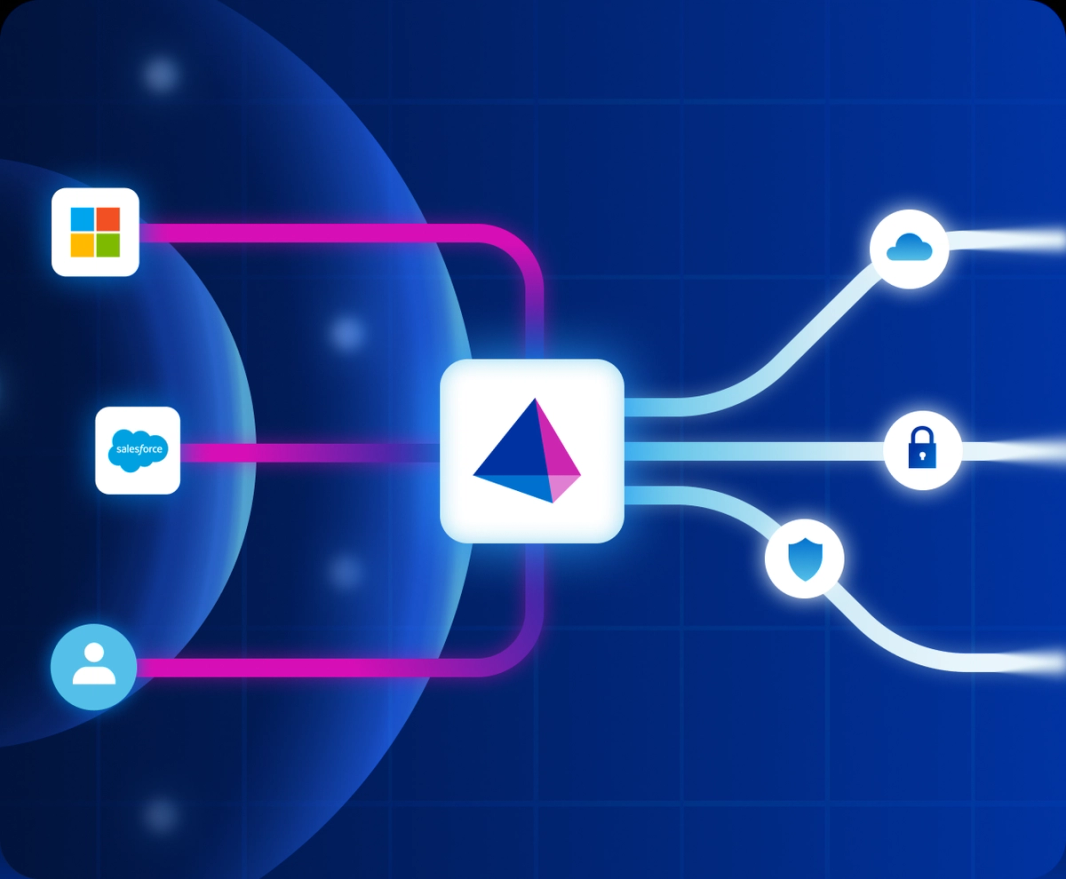
Unified application connectivity
Govern and secure any identity's access to your complete application landscape through a unified and adaptive approach to connectivity.
- Automate the identity lifecycle for secure access to disconnected apps with ease.
- Bring web service apps under full governance in minutes with the connectivity agent.
- Onboard hundreds of applications in a few clicks using express setup.
Additional Announcements
New enhancements
SailPoint IdentityIQ 9.0
Deliver essential risk reduction, performance upgrades, and modern UX for on-premises governance.
JIT Activation Policy
Implement conditional security frictions—business justification, re-auth, and service ticket checks.
Data Access Security
Ingest data classification labels from third-party DSPM tools including Microsoft Purview and BigID.
Effective privilege
Gain visibility into inherited privilege levels across nested groups and access structures.