Solution brief
Govern AI agency before it becomes an attack vector
See how SailPoint-Entro discovers shadow AI, governs agent lifecycles, and monitors intent with AIDR so you can scale agentic AI safely
Summary
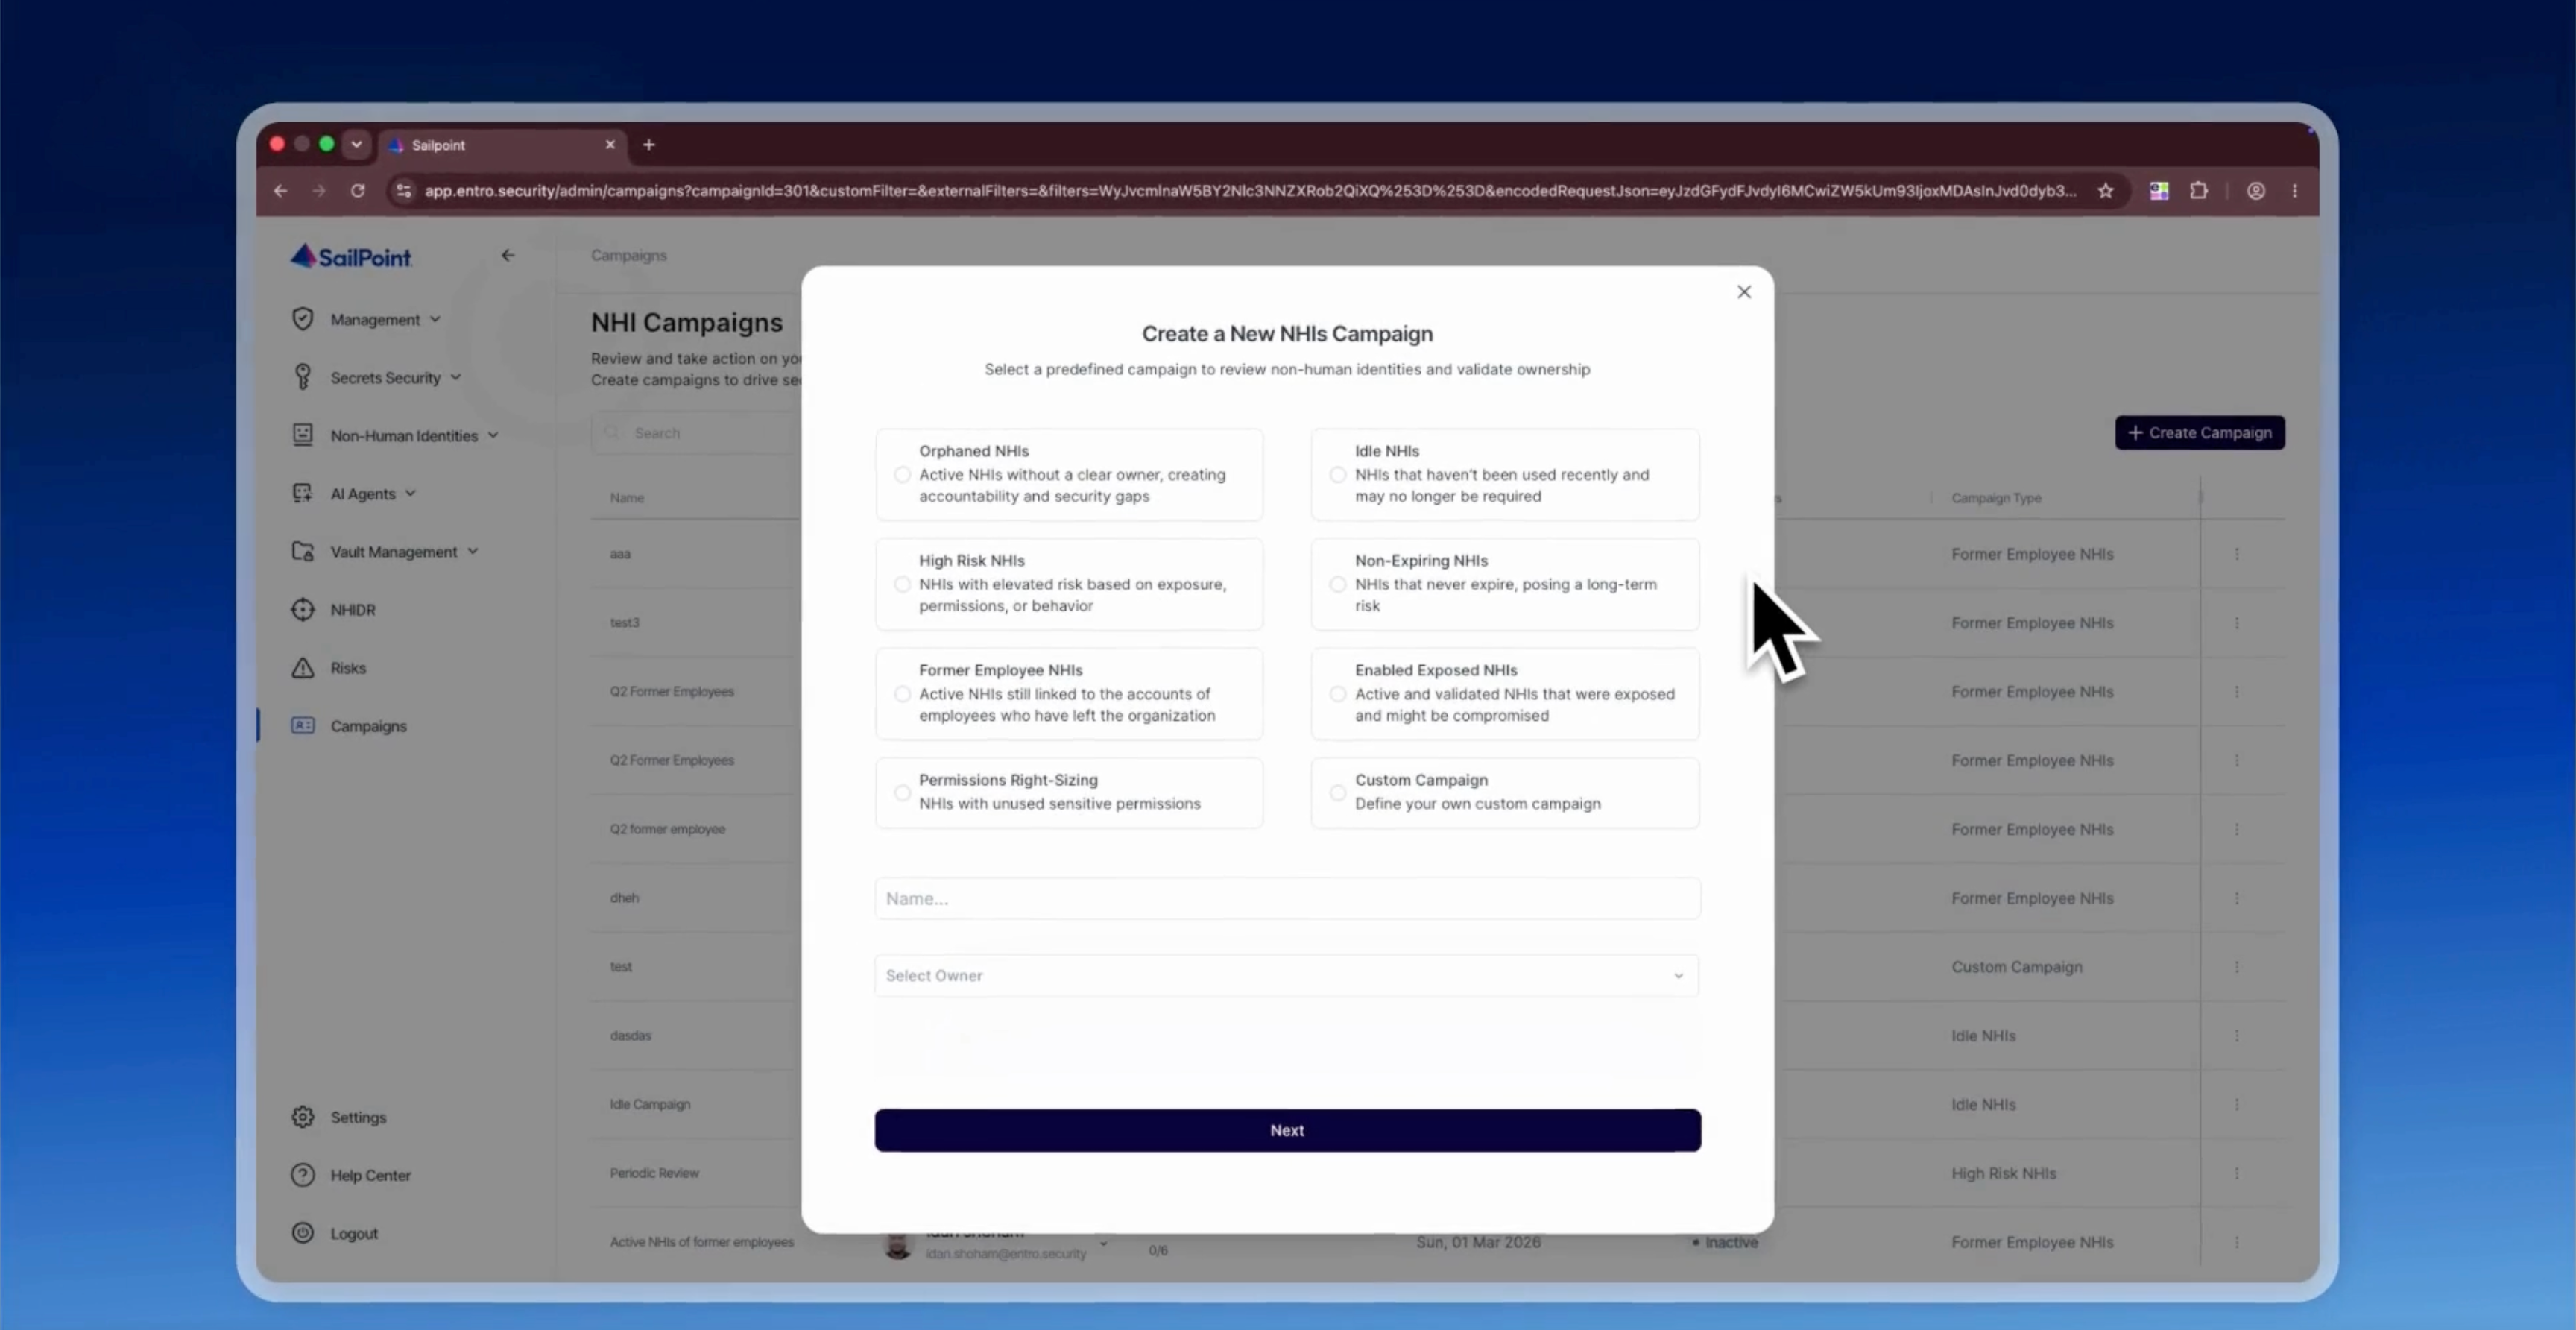
AI agents now operate autonomously across cloud, SaaS, endpoints, and developer toolchains. They can spin up without approval, connect to sensitive systems, and take actions no one authorized — leaving security teams with agent sprawl, no audit trail for actions and tool calls, and intent with no governance layer. This solution brief shows how SailPoint-Entro discovers every AI agent and MCP server in your environment, attributes ownership, and enforces governance across every agent and the identities behind them. Use it to adopt agentic AI at scale without losing control — from AWS, Azure, GitHub, and Salesforce to Claude Code, MCP-connected tools, and beyond.
You'll learn how to:
- Why CISOs rank AI agent security a top pain point
- How to discover shadow AI, agents, and MCP servers
- How AGA maps ownership and governs agent access
- How AIDR monitors intent to stop agent misuse
Topics
- AI & machine learning
- Machine identities
- Lifecycle management
Related resources
More to explore

Get started
Put adaptive identity to work
See how SailPoint sets the standard for identity security—helping enterprises reduce risk, scale with confidence, and stay ahead of what's next.