Blog
From AI agent visibility to risk mitigation: What’s new for SailPoint Agentic Fabric
When we launched SailPoint Agentic Fabric, we set out to solve a critical governance gap. As highlighted in our Horizons of Identity Security report, while 79% of organizations now run AI agents in production, a mere 2% use identity security tools designed to manage them. Since our initial announcement, the deployment of these autonomous agents has only accelerated—and so has the risk of roque agents operating with forgotten, unmonitored, or stolen credentials.
AI agents are not just static scripts; they dynamically reason, select tools, assume credentials, and query data across enterprise systems. To govern them effectively, security teams must be able to answer key questions in real time: What agents exist? Who is accountable for them? What data can they reach? And what happens when their risk profile changes?
To help organizations scale AI innovation safely, we have enhanced the foundational Discover and Governance capabilities of the Agentic Fabric and are introducing advanced Protect capabilities to deliver proactive risk mitigation.
SailPoint's approach: govern the path, not just the agent
With the General Availability announcement of SailPoint Agentic Fabric at Navigate London, we are delivering on our promise to secure enterprise AI innovation, now supercharged by the integration of the core capabilities from our acquisition of Entro. As part of the SailPoint Identity Security solution, Agentic Fabric works alongside SailPoint Human Fabric to provide a unified governance foundation for both human and non-human identities.
Our strategy is to govern the entire path of an AI agent’s actions, not just the agent itself. To achieve this, Agentic Fabric models each agent within the SailPoint Identity Graph and lineage map, establishing a complete relational chain across its human owner, credentials, entitlements, MCP servers, tools, and the enterprise data it can reach.
What this looks like in practice
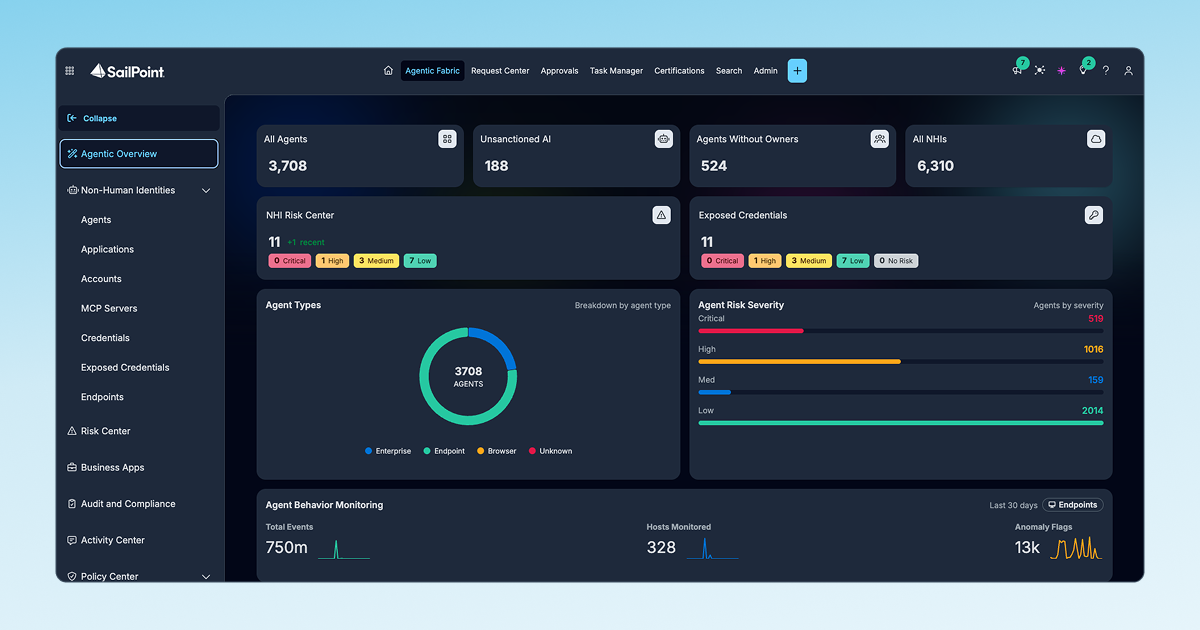
Discover: see the full agentic surface area, not just the agent
Agents appear wherever employees work or teams build them, from cloud platforms and SaaS applications to developer endpoints and browser-based AI tools. That includes shadow AI that employees have adopted without IT's knowledge. Agentic Fabric discovers agents through endpoint and browser sensors, supported cloud and SaaS sources, and SIEM and XDR telemetry. SailPoint then catalogs agents, MCP servers, machine accounts, and credentials in a unified registry. The credential inventory surfaces idle, unrotated, non-expiring, and former-employee credentials across more than 1,200 types.
A registry is still a list. The Identity Graph translates that inventory into actionable intelligence and governance workflows. That is the difference between knowing an agent exists and knowing what it could expose.
Govern: anchor every agent to a human owner
Ownership is easy to assign when an agent is created and easy to lose afterward. Agentic Fabric automatically discovers owners before building an ownership model with primary owners, secondary co-owners, and auto-assigned governance groups, so an agent doesn't become orphaned when its owner or builder moves on. Owners get a self-service portal to see their agents and machine accounts, request access changes, and keep ownership details current.
From there, agents enter the same governance workflows identity teams already know and trust. Access to agents, applications, and machine accounts runs through request and approval workflows, and agents join recurring certification campaigns. Centralized lifecycle controls provide one-click activation, deactivation, and decommissioning. Framework-aligned reporting turns that activity into evidence that helps support audit preparation under emerging AI standards and privacy regulations.
Protect: understand and mitigate risk
As a major advancement for SailPoint Agentic Fabric, we are introducing our new protect capabilities designed to give organizations the guardrails they need to drive safe, scalable AI innovation without compromising security.
- Risk center: The centralized risk center aggregates security findings across your cloud, SaaS, code, and CI/CD pipelines into a single queue. Risks are categorized into three actionable types—posture (hygiene and configuration gaps), exposure (leaked credentials), and threat (unusual runtime behavior)—for rapid remediation.
- Real-time behavior monitoring and anomaly detection: Rather than relying on static alert thresholds, Agentic Fabric establishes history-aware behavioral baselines for AI agents. By analyzing your existing EDR and SIEM telemetry, it monitors session activity, tool invocations, and network events—flagging abnormal behaviors, such as an agent suddenly connecting to unfamiliar servers outside of working hours.
- Inline prompt and response security: To prevent sensitive data exposure, Agentic Fabric intercepts user prompts and tool responses before they leave the endpoint or browser. It automatically scans for and redacts credentials, PII, and PHI in real time before they reach third-party LLMs like ChatGPT or Claude—allowing developers and employees to stay productive without compromising security.
- Automated risk workflows and enforcement: When critical threats or credential exposures are validated, automated risk workflows trigger immediate remediation. This includes blocking individual app-based endpoint agents with a one-click kill switch or executing policy-driven access deactivation, instead of waiting for the next manual review cycle.
Packaging updates
To provide a clear path for governing AI agents, our updated packaging is designed to meet you where you are on your Identity Security journey. These updated standalone offerings and suites allow organizations to start with dedicated non-human governance or seamlessly unify AI agent security within their existing SailPoint program.
SailPoint Agentic Fabric is a standalone solution for customers who only want non-human governance for their AI Agents and non-human identities (NHI). These standalone solutions deliver Discover, Govern, and Protect capabilities for AI Agents and NHI only. They are tiered into three main offerings:
| Standalone solution | Details |
|---|---|
| SailPoint Agentic Fabric - Standard | Visibility and ownership for every AI agent and NHI |
| SailPoint Agentic Fabric - Essentials | Governance for AI agents and NHIs |
| SailPoint Agentic Fabric - Advanced | Risk insight and SOC response for AI agents and NHIs |
Agentic Fabric Advanced customers that need premium Protect capabilities for their NHIs can also purchase the SailPoint Agentic Fabric - Protect add-on, which is available exclusively to Agentic Fabric Advanced customers.
SailPoint Agentic Suites are for customers who want a unified offering for both human and non-human governance. These Suites are enhanced with additional capabilities for non-human identities (NHIs). The Suites are tiered into three main packages:
| Package | Details |
|---|---|
| Agentic Standard | Core identity governance plus discovery for every AI agent and NHI. |
| Agentic Business | The Least Standing Privilege (LSP) foundation for human and agent identities. |
| Agentic Business Plus | Enforce zero standing privilege for all identities with just-in-time access. |
Agentic Business Plus customers that want premium Protect capabilities for their NHIs can also purchase the Non-Human Identity Protect add-on, which is available exclusively to Agentic Business Plus customers.
Where to start
Enterprises don't have to choose between adopting AI agents and keeping accountable control of access. The practical goal is to make every agent known, owned, and bounded, so security helps drive AI innovation with the context and control required to keep the organization safe.
See it for yourself. Take Agentic Fabric for a test drive in a dedicated demo environment. You and your team can explore how it discovers and maps agents to their owners, credentials, and data, with no connection to your production systems.
